Google Bans Chinese Hardware Maker After 1.3 Million Devices Turned Into Botnet
Videostrong Technology built backdoors into Android TV boxes for years, selling access to criminal networks before Google severed the partnership and dismantled the infrastructure
A Supply Chain Breach Years in the Making
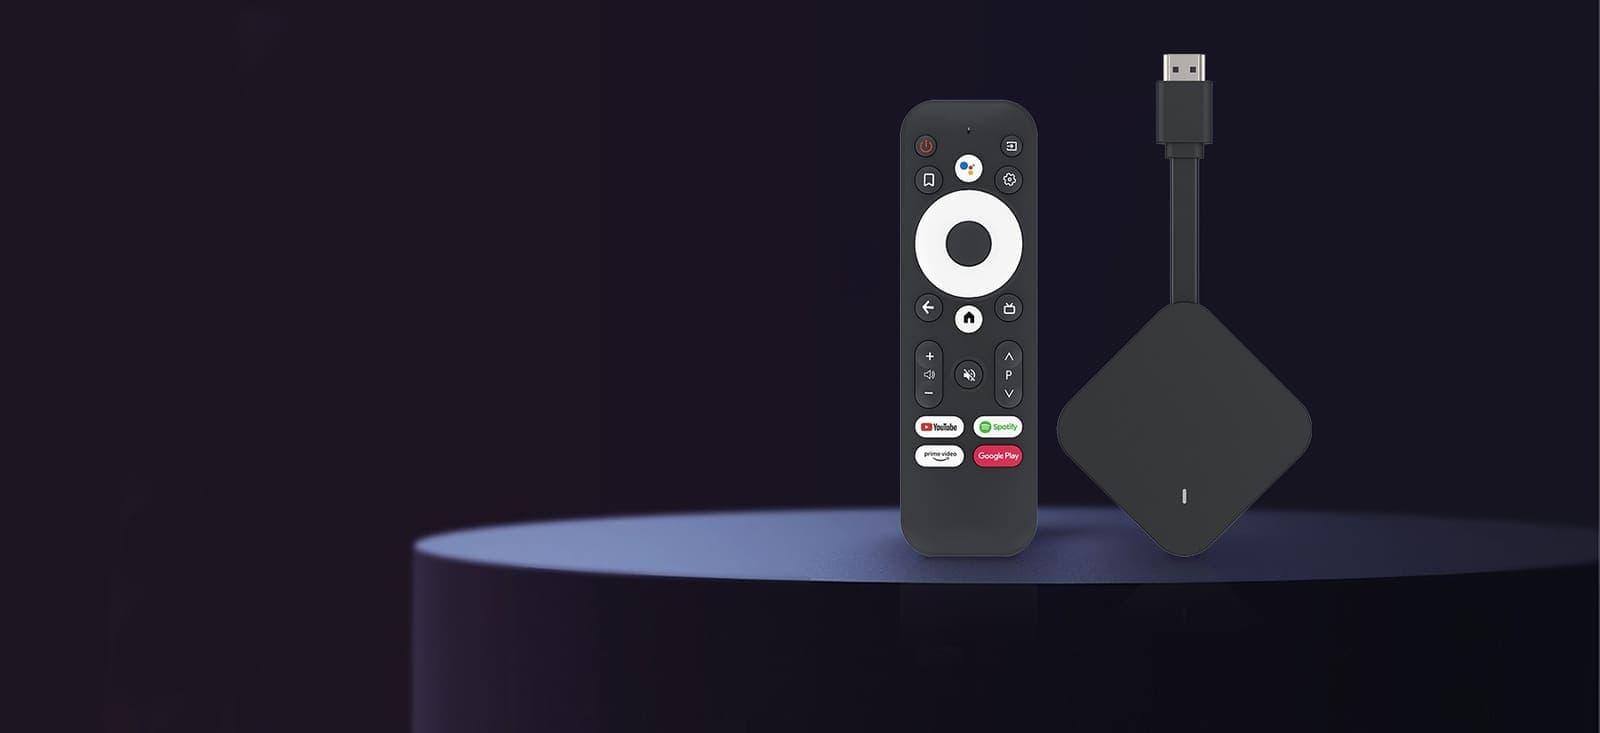
Google has terminated its partnership with Shenzhen-based Videostrong Technology Co. after discovering the manufacturer deliberately embedded backdoors in 1.3 million Android devices, transforming consumer hardware into a criminal botnet. The devices - primarily Android TV set-top boxes but also telehealth equipment, karaoke machines, and digital signage - operated without their owners' knowledge as nodes for ad fraud, data theft, and unauthorised network routing.
The scale suggests this was not a one-off lapse. According to Google, the malware appeared "built directly into many different device models and brands over multiple years," indicating systematic integration rather than isolated compromise. Videostrong deployed obfuscation techniques that loaded the malicious code only after users booted their devices for the first time, delaying detection and complicating forensic analysis.
At Opentechwire, we've tracked supply chain security failures across Asia's manufacturing hubs for years, but intentional sabotage by a certified partner represents a different order of risk. The Android ecosystem relies on a tiered certification model where Google vets manufacturers for compliance with security and compatibility standards. Videostrong held that certification until this incident, meaning the backdoor passed through multiple review checkpoints before reaching consumers.
The Business Model Behind the Backdoor
Google alleges Videostrong monetised the backdoor by selling access to what it calls "criminal affiliates," who then loaded secondary malware modules onto compromised devices. The company describes a layered operation: Videostrong provided the initial infrastructure, while affiliate operators ran specific schemes on top of it.
Those schemes included ad fraud - where infected devices generate fake ad impressions to siphon advertising budgets - and silent enrolment into residential proxy networks. The latter is particularly lucrative. Residential proxies route internet traffic through consumer devices to mask the origin of requests, making them valuable for scraping data, bypassing geo-restrictions, and evading anti-fraud systems. Legitimate proxy services exist, but involuntary enrolment turns consumer hardware into unwitting infrastructure for operations that often violate platform terms of service.
The financial incentive is clear. Residential proxy bandwidth trades at premium rates because it appears to originate from real households rather than data centres. By embedding backdoors at the manufacturing stage, Videostrong effectively converted hardware sales into recurring revenue from botnet access - a shadow business model running parallel to its legitimate operations.
Google also disrupted command-and-control domains operated by the affiliate networks, a move it estimates severed access to at least 10 million additional compromised devices. That figure suggests the affiliates distributed their modules through multiple channels beyond Videostrong's hardware, indicating a broader ecosystem of compromised Android and IoT devices.
Certification Revoked, Review Process Overhauled
Videostrong is now banned from building or selling certified Android devices and from supplying software for the platform. The ban is permanent unless Google reverses it, which seems unlikely given the company's characterisation of the backdoor as intentional and profit-driven.
Google has also revised its review process for device manufacturers, though it has not disclosed specifics. The challenge is inherent to the Android model: Google certifies partners but does not manufacture most devices itself, creating dependencies on third-party factories scattered across Shenzhen, Dongguan, and other manufacturing clusters. Auditing firmware at scale is resource-intensive, and obfuscation techniques can hide malicious code until runtime.
This incident will likely accelerate Google's efforts to tighten hardware attestation and runtime integrity checks. The company already requires certified devices to pass Compatibility Test Suite evaluations and to implement verified boot, but those measures focus on preventing unauthorised modifications after manufacture. Videostrong's backdoor was baked in before the device left the factory, a scenario that existing safeguards were not designed to catch.
The Wider IoT Security Problem
The botnet extended beyond entertainment devices into telehealth equipment and digital signage, categories where security failures carry different stakes. Telehealth devices often handle sensitive patient data, and their compromise could expose protected health information or disrupt remote monitoring. Digital signage, meanwhile, is increasingly used in corporate and public environments where network access can provide lateral movement into broader systems.
The diversity of affected device types underscores a persistent problem in the IoT sector: security is often an afterthought in hardware with thin margins and short development cycles. Android TV boxes, in particular, occupy a crowded market where manufacturers compete on price and feature count rather than security posture. Videostrong's ability to maintain certification while embedding backdoors suggests that review processes, however rigorous on paper, struggle to keep pace with deliberate evasion.
The incident also raises questions about downstream liability. Consumers who purchased Videostrong devices had no way to detect the backdoor and no reason to suspect a Google-certified partner. Retailers and distributors that carried the hardware are unlikely to face consequences, but the reputational damage to the Android TV brand is real. Trust in certification marks depends on the assumption that certified products meet baseline security standards; breaches like this erode that assumption.
What Comes Next for Android Certification
Google's decision to sever ties and publicly name Videostrong sends a signal to other partners, but enforcement will depend on the company's ability to detect similar schemes before they scale. The 1.3 million figure represents devices Google confirmed were compromised; the true number may be higher if obfuscation delayed discovery on some models.
The company's move to disrupt affiliate command-and-control infrastructure is significant. Taking down C2 domains is a standard response to botnets, but doing so in coordination with a partner ban suggests Google is treating this as both a supply chain failure and an active threat operation. The 10 million additional devices mentioned in Google's statement indicate that the affiliates were sophisticated operators with diversified infection vectors, not opportunistic actors relying solely on Videostrong's backdoor.
For manufacturers still in good standing, the incident is a reminder that certification is conditional. Google's willingness to publicly ban a partner and attribute intent - using language like "intentionally developed, deployed, and operated for financial gain" - suggests it will not treat future breaches as accidental lapses. That posture may push some manufacturers to invest in more robust internal security audits, though cost pressures in the low-end device market will continue to work against that.
The Android ecosystem's openness is a strength in terms of hardware diversity and price competition, but it also distributes security responsibility across hundreds of partners with varying capabilities and incentives. Videostrong's botnet is a case study in what happens when one of those partners decides the risk of getting caught is worth the revenue from selling backdoor access. Google has closed this particular channel, but the structural vulnerabilities that enabled it remain.