Forensics Firm Claims New Exploit to Bypass iPhone Inactivity Reboot
Magnet Forensics training materials suggest law enforcement tools can now maintain access to locked iOS devices despite Apple's 72-hour security timer.
The 72-Hour Window Narrows
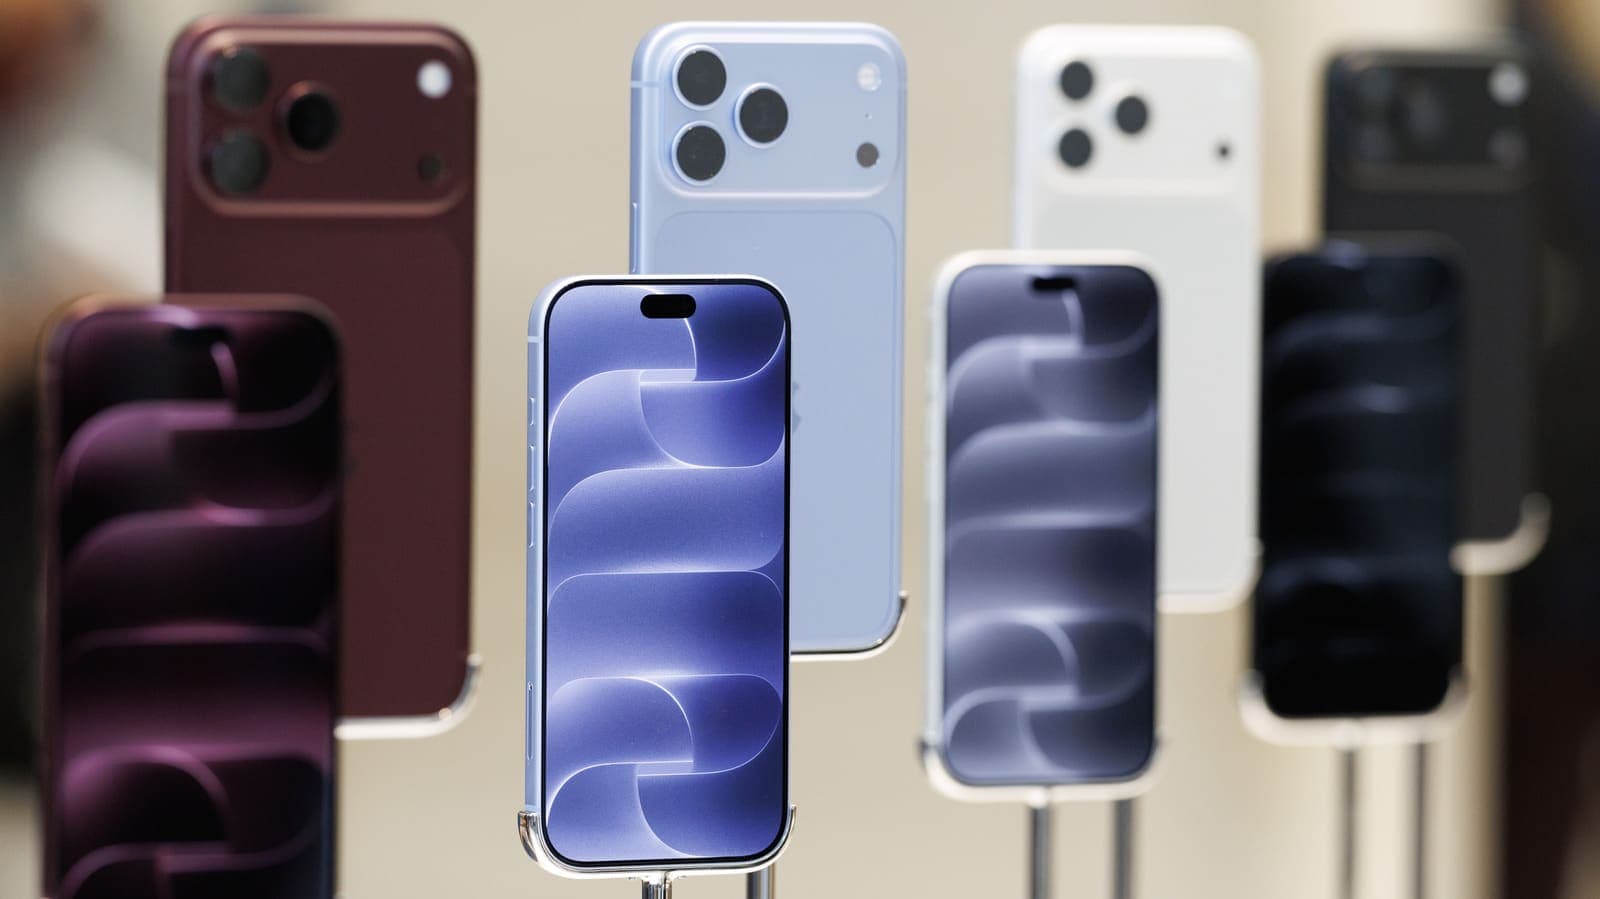
For two years, Apple's inactivity reboot has served as a backstop for device security. Introduced across the iPhone lineup in 2024, the feature forces a full restart if the handset remains locked for 72 consecutive hours. The restart pushes the device back into a Before First Unlock state, where the majority of user data sits encrypted and inaccessible to extraction tools. Law enforcement agencies worldwide have encountered this barrier repeatedly, particularly when attempting to access devices seized during investigations but not unlocked in time.
That window now appears shorter. Training materials produced by Magnet Forensics describe new capabilities in the company's GrayKey product line that allegedly allow investigators to hold an iPhone in an After First Unlock state even after the 72-hour threshold passes. The distinction between AFU and BFU is central to iOS forensics. In AFU, the device has been unlocked at least once since boot, and a subset of encryption keys remains in memory. In BFU, nearly all data is locked behind keys that exist only when the user enters a passcode. The inactivity reboot was designed to force devices from AFU back to BFU automatically, closing the forensic window.
Magnet's training video, obtained and reviewed by 404 Media, shows employees explaining that two new features, GrayKey Preserve and an Evidence Preservation Mode, can prevent that regression. One representative describes the development as transformative for mobile forensics. The video does not disclose the technical mechanism, but the implication is clear: Magnet has found a method to keep the device in AFU regardless of elapsed time or reboot triggers.
What Stays in Memory
The AFU state is valuable to investigators because certain categories of data remain decrypted in volatile memory. Messages sent or received after the last unlock, location cache entries, recently deleted photos awaiting permanent removal, and app session tokens all fall into this category. Apple's inactivity reboot was intended to flush that cache by forcing a cold start. If Magnet's tools can inhibit the reboot or restore AFU status immediately afterward, those data types remain accessible far longer than Apple intended.
Magnet's training materials also claim the new features can block automatic data deletion routines built into iOS. The operating system purges certain cached location records after a set interval, typically between seven and 30 days depending on the data type. Recently deleted iMessages and photos are likewise scheduled for permanent removal after 30 days. According to the video, GrayKey Preserve can prevent these deletions from executing, effectively freezing the state of the device for forensic purposes.
The technical implications are significant. If the tool manipulates system timers or interrupt routines to delay or cancel scheduled tasks, it represents a deeper level of access than previous GrayKey iterations, which primarily focused on passcode bypass. If instead it exploits a flaw in how iOS handles reboot conditions, Apple will likely issue a patch once the vulnerability is documented.
GrayKey's Expanding Reach
Magnet Forensics acquired Grayshift, the original developer of GrayKey, in 2021. The device itself is a small box that connects to an iPhone via Lightning or USB-C and attempts to brute-force the passcode or exploit known vulnerabilities. Its customer base consists almost exclusively of law enforcement and government agencies. Pricing details are not public, but industry estimates place annual licences in the range of tens of thousands of dollars per seat.
The company has historically avoided public discussion of its methods, a common stance among vendors in the lawful-access market. Exploits disclosed too widely lose effectiveness once device manufacturers patch the underlying flaws. Magnet's decision to produce training videos for customers is standard practice in the sector, but the leak of those materials into public view is less common. The video obtained by 404 Media appears to have been intended for internal distribution among law enforcement clients, not for publication.
Magnet Forensics has not responded to requests for comment on the authenticity of the video or the capabilities described within it. Apple likewise declined to comment on whether the company is aware of the claimed exploit or has begun work on a countermeasure.
The Legal and Technical Arms Race
At Opentechwire, we've tracked the forensics-versus-encryption cycle through multiple iterations. Each time a device manufacturer strengthens encryption or introduces new lockout features, forensic vendors respond with updated tools. Apple introduced the Secure Enclave Processor in 2013, rate-limiting passcode attempts and binding encryption keys to hardware. GrayKey emerged in 2017 as a workaround. Apple tightened USB access in 2018 with USB Restricted Mode, which disables the Lightning port after one hour of inactivity. GrayKey adapted. The inactivity reboot in 2024 was Apple's latest move. Magnet's new tools suggest that cycle continues.
The legal framework surrounding these tools remains fragmented. In most jurisdictions, law enforcement can compel a suspect to unlock a device using biometrics such as Face ID or Touch ID, but cannot compel disclosure of a passcode, which is considered testimonial and protected under various constitutional or statutory provisions. Tools like GrayKey circumvent that distinction by removing the need for user cooperation. Courts in the United States, the European Union, and parts of Asia have issued conflicting rulings on whether such access constitutes a search requiring heightened judicial oversight.
Privacy advocates argue that tools capable of bypassing device encryption undermine the security of all users, not just those under investigation. If a vulnerability exists that allows forensic access, it can potentially be discovered and exploited by malicious actors as well. Apple has consistently maintained that it will not build backdoors into its products, even when requested by government agencies. The company's position is that strong encryption protects users from a wide range of threats, including state-sponsored hacking, organised crime, and corporate espionage.
What Investigators Gain and Users Lose
For investigators, the ability to maintain AFU access extends the practical window for extracting evidence from seized devices. In cases where a phone is recovered days or weeks after an incident, the difference between AFU and BFU can determine whether messages, location data, or app activity can be retrieved. Prosecutors in criminal cases have cited the inability to access locked phones as a recurring obstacle, particularly in cases involving encrypted messaging apps that store data locally rather than in the cloud.
For device owners, the development erodes one of the few certainties in mobile security: that a device left untouched for three days will lock itself down. Users who rely on that feature for protection, whether from state surveillance, corporate espionage, or theft, now face a narrower margin. The inactivity reboot was designed to operate silently and automatically, requiring no user action. If that mechanism can be defeated, users have no fallback short of powering down the device manually or disabling biometric unlock entirely.
The broader question is whether consumer encryption can coexist with lawful access. Magnet Forensics and similar vendors argue that their tools serve legitimate investigative needs and are sold only to vetted government customers. Privacy researchers counter that any tool capable of bypassing encryption represents a systemic risk, regardless of the buyer's intentions. The debate is unlikely to resolve soon, but each new capability shifts the balance incrementally in favour of access over privacy.
Waiting for Apple's Response
Apple's typical response to forensic exploits is silence followed by a patch. The company rarely acknowledges vulnerabilities in public until a fix is available, a policy intended to limit the window during which attackers can exploit known flaws. If Magnet's tools rely on a software vulnerability, an iOS update could render them ineffective within weeks. If the method involves hardware manipulation or a design limitation in the Secure Enclave, a fix may require changes that appear only in future iPhone models.
The training video's existence suggests Magnet believes its new capabilities are durable enough to justify customer training and deployment. Whether that confidence is warranted will depend on how quickly Apple can reverse-engineer the technique and deploy a countermeasure. In the meantime, the 72-hour reboot window that users have relied on since 2024 is no longer a guarantee.