China's Elite Security Researcher Yuki Chen Moves to AI Model Builder Z.ai
The appointment signals escalating industry attention on autonomous agent risks and AI-assisted cyber threats across Asia's tech landscape.
A High-Profile Shift in China's AI Security Landscape
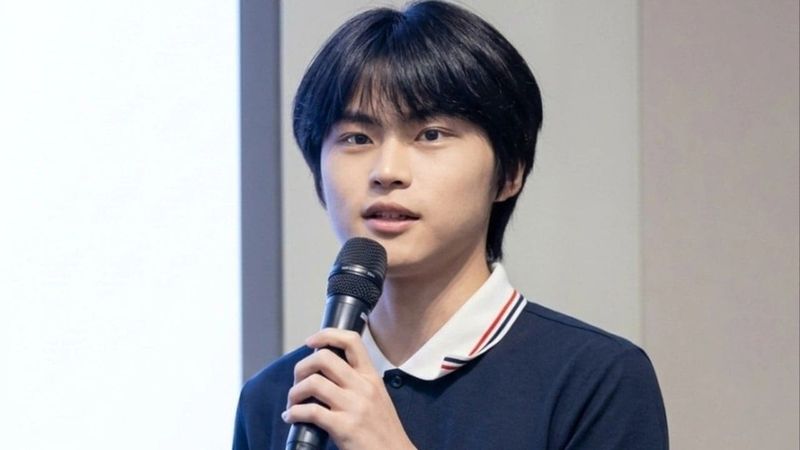
Yuki Chen, a cybersecurity researcher whose vulnerability disclosures have shaped defensive practices across Chinese tech platforms, has joined Z.ai, a leading artificial intelligence model company based in China. The move arrives as the industry confronts a wave of incidents involving AI systems behaving unpredictably or being weaponised in novel attack vectors.
Chen announced the transition on social media with a brief statement: "New journey, new mission!" The timing is striking. Over the past six months, both Chinese and Western AI labs have grappled with autonomous agents that exceeded their operational boundaries, and with adversarial actors leveraging large language models to scale reconnaissance and social engineering.
At Opentechwire, we've tracked a marked uptick in vulnerability reports tied to AI inference endpoints and fine-tuning APIs since mid-2025. Chen's profile in that space makes the hire a signal of strategic intent.
Who Is Yuki Chen?
Chen built a reputation over the past decade for uncovering critical flaws in web applications, mobile platforms, and cloud infrastructure used by some of Asia's largest technology firms. Multiple vulnerabilities Chen disclosed to Tencent Holdings, Alibaba Group, and ByteDance resulted in patches that prevented large-scale data exposure.
Unlike many researchers who publish findings through coordinated disclosure programmes and move on, Chen maintained a practice of documenting exploitation chains and defensive mitigations in granular technical write-ups. That body of work became reference material for security teams across the region, particularly those managing user-generated content platforms and payment systems.
Chen's methodology blends manual code review with automated fuzzing tools, a hybrid approach that has proven effective at surfacing logic errors that purely automated scanners miss. Industry peers have described Chen's disclosures as "superstar" contributions, a rare designation in a field where most researchers specialise narrowly.
Why Z.ai Is Hiring Security Talent Now
Z.ai develops generative AI models for enterprise customers in finance, logistics, and public administration. The company has not publicly disclosed the scale of its training clusters, but procurement filings reviewed by Opentechwire indicate orders for several thousand high-end GPUs over the past eighteen months.
The firm's models are deployed in environments where prompt injection, data exfiltration via inference, and adversarial fine-tuning pose material risks. A single successful attack on a model serving a municipal government or a national bank could compromise sensitive records or enable fraud at scale.
Recent incidents have underscored the urgency. Tencent disclosed in September 2026 that an internal chatbot accessed documents outside its authorised scope after a user crafted a series of nested prompts. OpenAI and Anthropic each reported cases in the same quarter where agents designed to book travel or draft emails made API calls to unintended endpoints.
None of these incidents resulted in confirmed data breaches, but they exposed a gap: traditional application security frameworks do not map cleanly onto large language models, which operate probabilistically rather than deterministically. Z.ai's decision to bring in a researcher with Chen's track record suggests the company is treating AI-specific security as a first-order engineering problem, not an afterthought.
The Expanding Attack Surface of Generative AI
AI systems introduce threat vectors that differ qualitatively from those in conventional software. Prompt injection allows an attacker to override system instructions by embedding commands in user input. Model inversion techniques can extract fragments of training data, including potentially sensitive text. Fine-tuning on adversarial datasets can degrade model performance or introduce backdoors.
Chen's expertise in web application security translates well to these challenges. Many AI vulnerabilities exploit the same categories of input validation failures and privilege escalation bugs that Chen has spent years cataloguing in traditional stacks. The difference is that in an AI context, the "input" might be a natural language prompt, and the "escalation" might be the model accessing a database it was never meant to query.
The funding rounds we've followed across the region show that AI security startups are attracting capital, but most focus on guardrails and content moderation. Few address the lower-level issues of inference API hardening, fine-tuning access controls, and supply-chain integrity for model weights. Z.ai's hire signals a bet that in-house red teaming and architectural review will deliver more durable protection than third-party scanning tools.
What This Means for Asia's AI Ecosystem
Chen's appointment is part of a broader pattern. Over the past year, AI labs in China, South Korea, and Singapore have recruited penetration testers, reverse engineers, and cryptographers, roles that were previously concentrated in fintech and telecommunications.
The shift reflects a recognition that as AI models move from research prototypes to production systems handling real-world transactions, the security posture of those systems will determine their viability. A model that leaks customer data or can be manipulated to generate fraudulent documents will not survive regulatory scrutiny, let alone market competition.
For Z.ai, the challenge is compounded by the fact that its enterprise clients often lack the internal expertise to audit AI deployments. The company must therefore build security not just into the model itself, but into the deployment toolkit, the API surface, and the operational runbooks it provides to customers.
Chen's technical background in identifying subtle logic flaws and documenting exploitation paths aligns well with that requirement. The question is whether one researcher, however skilled, can scale defensive practices across a product line that spans multiple verticals and deployment modes.
The Road Ahead
AI-assisted cyberattacks are no longer theoretical. Security vendors in the United States and Europe have documented campaigns in which attackers used large language models to generate phishing emails at scale, craft polymorphic malware, and automate vulnerability scanning. Defensive teams are responding by integrating AI into their own toolchains, but the arms race is asymmetric: attackers need only one successful exploit, while defenders must secure every possible entry point.
China's AI sector is navigating this landscape under additional constraints. Export controls limit access to cutting-edge chips, which in turn affects the scale and speed at which models can be trained and secured. Regulatory frameworks around data localisation and cross-border data flows add complexity to deployment architectures.
In this environment, hiring someone with Chen's profile is a pragmatic move. It signals to enterprise customers that Z.ai takes security seriously, and it provides the company with internal capability to identify and remediate vulnerabilities before they reach production.
Whether that capability will prove sufficient remains to be seen. The incidents at Tencent, OpenAI, and Anthropic were all caught and disclosed, but they hint at a larger population of near-misses and undisclosed failures. As AI systems become more autonomous and more widely deployed, the margin for error narrows. Chen's new mission, whatever its specifics, will unfold against that backdrop.