Defence Systems Cannot Keep Up With AI-Enabled Hacking, Anduril Co-Founder Says
Palmer Luckey argues that legacy infrastructure is struggling to counter machine-learning-driven exploits, as North Korea and other adversaries exploit the capability gap
The Mismatch Between Attack and Defence
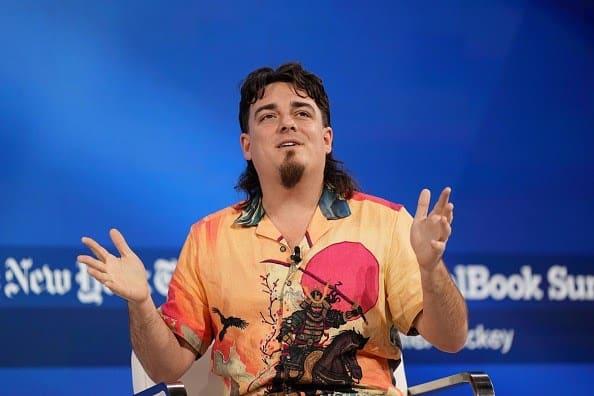
Organisations relying on legacy technology are finding themselves unable to counter the speed and sophistication of machine-learning-enabled intrusions, according to Palmer Luckey, co-founder of Anduril Industries and creator of the Oculus virtual reality headset. Speaking at a conference in New York on Wednesday, Luckey framed the problem as a structural imbalance: adversaries have adopted artificial intelligence to discover and exploit vulnerabilities faster than defenders can patch or harden their systems.
Luckey pointed to recent technical disruptions across multiple sectors as evidence of the widening gap. Government officials have attributed some of those incidents to organisations scrambling to apply fixes after AI-assisted reconnaissance identified previously unknown weaknesses. Yet Luckey's diagnosis went deeper, arguing that the real issue lies in the age and inflexibility of the infrastructure being targeted. Systems built decades ago were never designed to absorb updates at the pace now demanded by the threat landscape, and that architectural debt is coming due.
The observation arrives at a moment when the intersection of artificial intelligence and offensive cyber operations has moved from theoretical risk to operational reality. Machine-learning models can now automate reconnaissance, generate polymorphic malware and adapt exploit chains in real time, compressing attack timelines from weeks to hours. Defence, by contrast, remains a human-intensive process constrained by procurement cycles, compliance frameworks and the sheer inertia of installed base.
North Korea and the Strategic Dimension
Luckey named North Korea as one actor actively exploiting the capability mismatch, driven by both strategic and financial motives. The country has long used cyber operations as a force multiplier, compensating for conventional military and economic disadvantages with a well-resourced hacking apparatus. Over the past decade, Pyongyang-linked groups have stolen hundreds of millions of dollars from financial institutions, cryptocurrency exchanges and defence contractors, channelling proceeds back into weapons programmes and regime coffers.
The addition of AI tooling to that playbook represents a step change. Where earlier campaigns relied on labour-intensive spear-phishing and manual lateral movement, machine-learning models can now automate target selection, craft contextually plausible lures and identify high-value data stores without human supervision. The result is a higher volume of intrusions, executed faster and with fewer operators, making attribution harder and response windows narrower.
Luckey did not specify which other adversaries he had in mind, but the strategic logic applies across several theatres. China's Ministry of State Security and People's Liberation Army units have invested heavily in AI research, including applications for signals intelligence and network exploitation. Russia's military intelligence directorate has demonstrated a willingness to deploy disruptive cyber operations in support of kinetic campaigns, and AI-assisted reconnaissance would lower the cost and risk of pre-positioning access. Iran, too, has expanded its cyber capabilities over the past five years, targeting critical infrastructure in the Middle East and beyond.
The common thread is asymmetry. States with smaller defence budgets or limited access to advanced hardware can still field capable offensive cyber units, especially when AI lowers the skill floor for exploit development. That dynamic inverts the traditional calculus of deterrence, where defenders could rely on superior resources to outspend attackers. In the AI era, a handful of well-trained operators with access to open-source models can probe thousands of targets in parallel, while defenders must secure every endpoint, every application and every supply chain.
The Pace Problem
When asked how concerned the public should be, Luckey offered a conditional answer: it depends on how well prepared you are. He then added a cryptic warning that people would find out what is happening soon enough, a remark that suggested either imminent disclosures or a belief that the scale of compromise is not yet fully understood.
The exchange underscored a recurring theme in Luckey's remarks: the problem is not that AI makes systems unhackable or that defence is impossible, but that the tempo of change has outstripped institutional capacity to respond. Patching a vulnerability takes time. Validating a fix across heterogeneous environments takes longer. Rolling out that fix to air-gapped networks, legacy hardware or systems governed by strict change-control processes can take months. Meanwhile, adversaries iterate daily, testing new payloads against updated defences and discarding techniques that no longer work.
This tempo mismatch is particularly acute in sectors where uptime is critical and risk tolerance is low. Energy grids, healthcare systems, transportation networks and financial clearing houses all operate under regulatory regimes that prioritise stability over agility. A hospital cannot afford to take its electronic health record system offline for a week to rebuild the stack, even if that would eliminate a known vulnerability. A power utility cannot deploy an untested security patch during peak demand. The result is a patchwork of workarounds, compensating controls and deferred upgrades, each of which introduces new attack surface.
Luckey argued that organisations will have to accelerate their adoption cycles, but he did not elaborate on how that might be achieved without triggering the very disruptions defenders are trying to avoid. The tension is real: moving faster reduces the window of exposure but increases the risk of misconfigurations, compatibility failures and unintended downtime. Moving slowly preserves stability but leaves systems vulnerable to exploits that adversaries have already weaponised.
AI as a Defensive Tool
Luckey expressed optimism that artificial intelligence could eventually tilt the balance back in favour of defenders, provided they move quickly enough to deploy it at scale. The logic is straightforward: if machine learning can automate reconnaissance and exploit generation, it can also automate threat detection, anomaly analysis and incident response. Models trained on network telemetry can identify deviations from baseline behaviour faster than human analysts, correlate indicators across disparate data sources and recommend remediation steps in near real time.
Several large cloud providers and security vendors have already embedded machine-learning models into their platforms, using them to flag suspicious login patterns, detect lateral movement and quarantine compromised accounts. The results have been mixed. False-positive rates remain high in some environments, generating alert fatigue and eroding trust in automated systems. Adversaries, meanwhile, have begun to probe the decision boundaries of defensive models, crafting payloads that evade detection by staying just inside the threshold of normal behaviour.
The deeper challenge is that defensive AI requires high-quality training data, and most organisations do not have it. Attackers can train their models on public vulnerability databases, leaked source code and synthetic environments that mimic production systems. Defenders, by contrast, must work with incomplete logs, redacted incident reports and data sets that reflect only the attacks they have already detected, not the ones that succeeded unnoticed. That asymmetry in training data translates into an asymmetry in model performance, and it is not clear how defenders close the gap without fundamentally rethinking how they instrument and monitor their environments.
Luckey's assertion that advantages will accrue to the side most effectively using AI for defence is plausible in the long run, but it assumes that defenders can match the pace of offensive innovation. That assumption is far from guaranteed. Offensive tooling benefits from a permissive testing environment: attackers can iterate freely, fail cheaply and deploy without regulatory approval. Defensive tooling, by contrast, must meet compliance standards, integrate with legacy systems and operate under scrutiny from auditors, regulators and boards. The friction is structural, and it is not clear that exhortations to "pick up the pace" will overcome it.
What Comes Next
The conference exchange took place against the backdrop of a week marked by technical disruptions severe enough to force the cancellation of a scheduled appearance by the US Vice President, who was redirected to meetings on the matter. That detail, mentioned by the interviewer, underscores the seriousness with which senior officials are treating the current threat environment. When a sitting vice president cancels a public engagement to attend crisis discussions, the implication is that the problem has escalated beyond routine incident response.
Luckey's warning that "it's time to start running" captures the urgency, but it also raises questions about what running looks like in practice. For governments, it may mean accelerating procurement of next-generation security tools, relaxing some compliance requirements to enable faster patching, or investing in workforce development to train analysts who can operate AI-assisted defence platforms. For private-sector organisations, it may mean retiring legacy systems sooner than planned, accepting higher short-term costs in exchange for long-term resilience, or partnering with managed security providers who have the scale to deploy advanced tooling.
For adversaries, the incentive structure remains unchanged. As long as the capability gap persists, the returns on offensive cyber operations will continue to justify the investment. North Korea will keep stealing to fund its programmes. China will keep probing critical infrastructure to map dependencies and pre-position access. Russia will keep testing disruptive techniques in contested regions. And a growing cohort of criminal groups will keep deploying ransomware, knowing that many targets will pay rather than rebuild.
The question is whether defenders can compress their decision cycles enough to narrow the gap before the next wave of disruptions arrives. Luckey's remarks suggest that the answer is not yet clear, and that the cost of finding out may be higher than many organisations are prepared to accept.